Xinfeng Li
The Hong Kong Polytechnic University
General Chair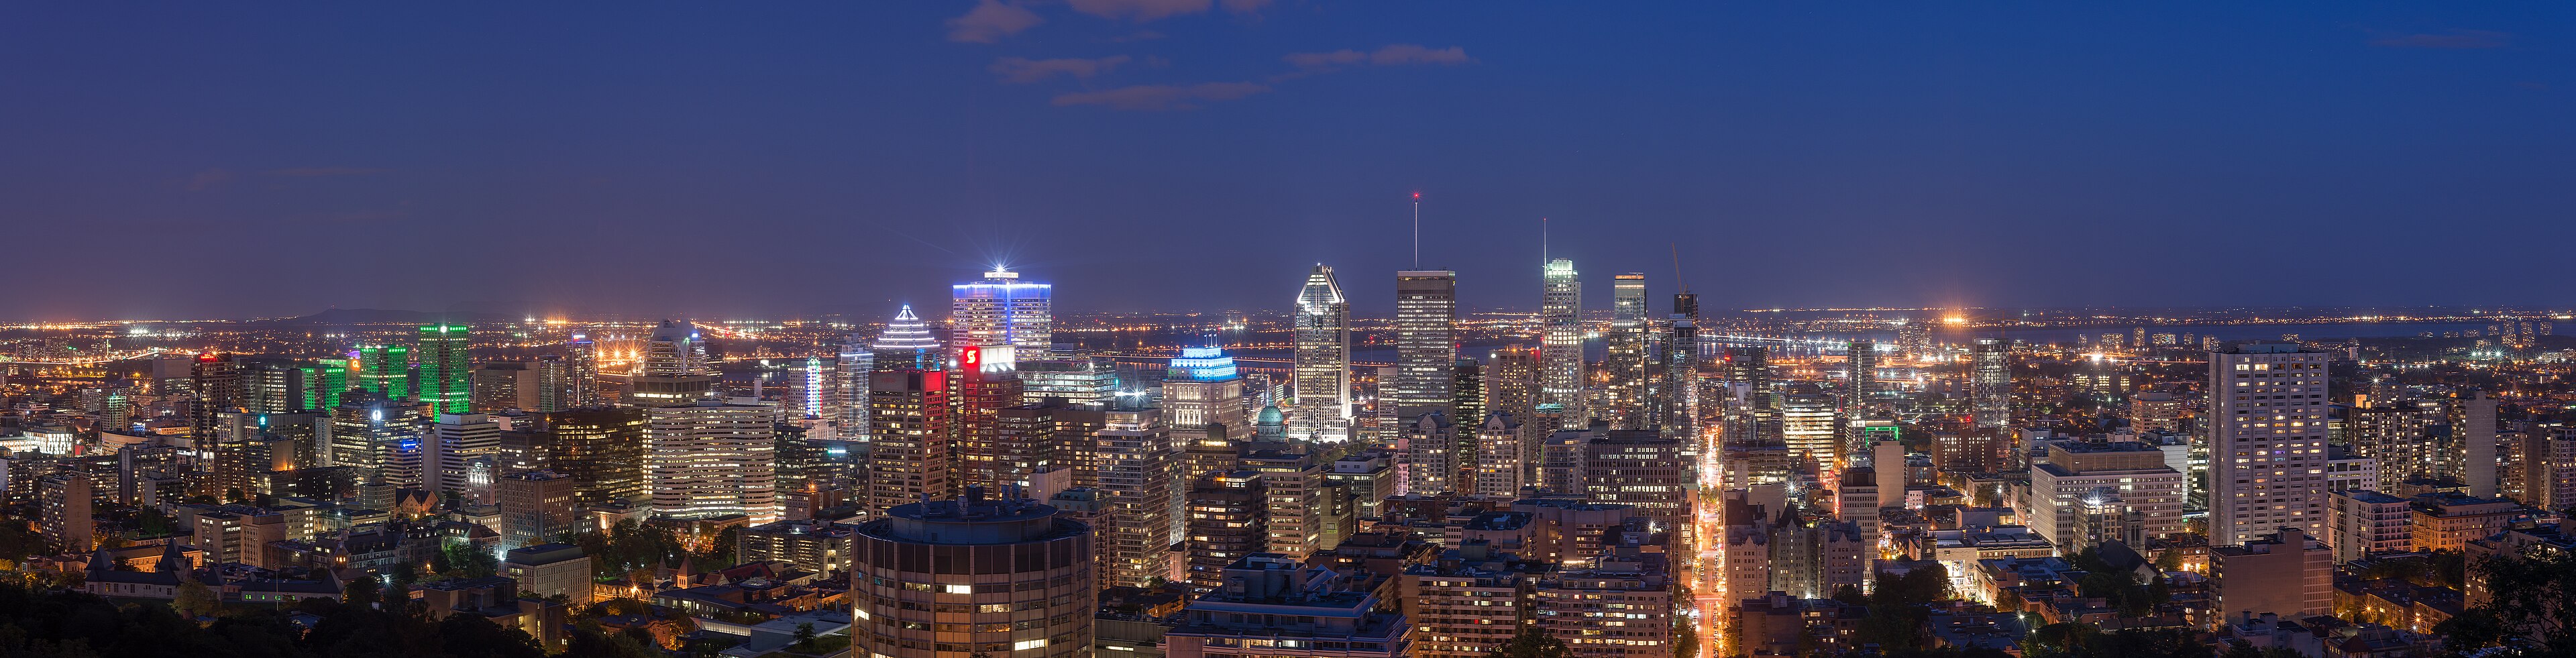
AAAI-27 Workshop
AAAI-27 · February 22 or 23, 2027
Montréal, Canada · Full-day, in person
Photo: Arild Vågen · CC BY-SA 4.0
A focused forum for understanding how autonomous language-model agents fail under adversarial pressure—and how to build systems that remain reliable when inputs, tools, and collaborators cannot be trusted.
LLM agents increasingly observe, remember, plan, coordinate, and act through external tools. These capabilities create attack surfaces across input channels, tool use, memory, identity, and multi-agent communication.
This workshop brings together researchers and practitioners working on realistic attacks, evaluations, secure agent architectures, and responsible defenses for agents operating in adversarial environments.
LLM Agents Under Threat in Cyberspace invites submissions from researchers and practitioners studying how autonomous LLM agents behave when their observations, memories, tools, identities, and collaborators may be adversarial or compromised. As agents gain the ability to browse the web, execute code, call APIs, use credentials, access external services, and coordinate with other agents, traditional language-model vulnerabilities can become concrete security failures with consequences beyond the model interface.
The workshop connects research on attacks, defenses, evaluation, and secure system design. We welcome empirical studies, new benchmarks, red-teaming methods, secure architectures, position papers, datasets, and lessons from deployed systems. We are especially interested in work that develops realistic threat models, evaluates end-to-end agent behavior, and proposes defenses that remain effective against adaptive attackers.
Topics include, but are not limited to:
Status: Submission instructions will be announced soon.
All times are local.
| Time | Activity |
|---|---|
| Morning Session | |
| Opening remarks (Welcome) | |
| Keynote 1 (Keynote) | |
| Paper session 1 (Research) | |
| Coffee break (Break) | |
| Invited talk 1 (Invited talk) | |
| Paper session 2 (Research) | |
| Afternoon Session | |
| Lunch break (Break) | |
| Keynote 2 (Keynote) | |
| Paper session 3 (Research) | |
| Coffee break & poster session (Poster) | |
| Invited talk 2 (Invited talk) | |
| Panel discussion (Panel) | |
| Closing remarks & award (Closing) | |
The Hong Kong Polytechnic University
General Chair
Carnegie Mellon University
Program Chair
University of Waterloo
Local Arrangements · Publications
City University of Hong Kong
Publicity
Tokyo University of Science
Student Organizer
The Hong Kong Polytechnic University
Student Organizer
University of Electronic Science and Technology of China
Student Organizer
ETH Zürich
Advisory Board
Duke University
Advisory Board
Carnegie Mellon University
Advisory Board
The University of Sydney
Advisory Board
The University of British Columbia
Advisory Board
Nanyang Technological University
Advisory BoardQuestions about scope or fit can be sent to llm-agents-under-threat@googlegroups.com.